Asos investigates cyber incident after hackers message app customers
Asos is probing an unauthorized notification sent to customers claiming its Snowflake data environment was compromised. The company stated payment-card data and passwords were not impacted.
- Headline: Asos investigates cyber incident after hackers message app customers
- Dispatch Summary: Asos is probing an unauthorized notification sent to customers claiming its Snowflake data environment was compromised. The company stated payment-card data and passwords were not impacted.
- Verification: Corroborated across independent reporting outlets with primary sources and real-time wire transmissions.
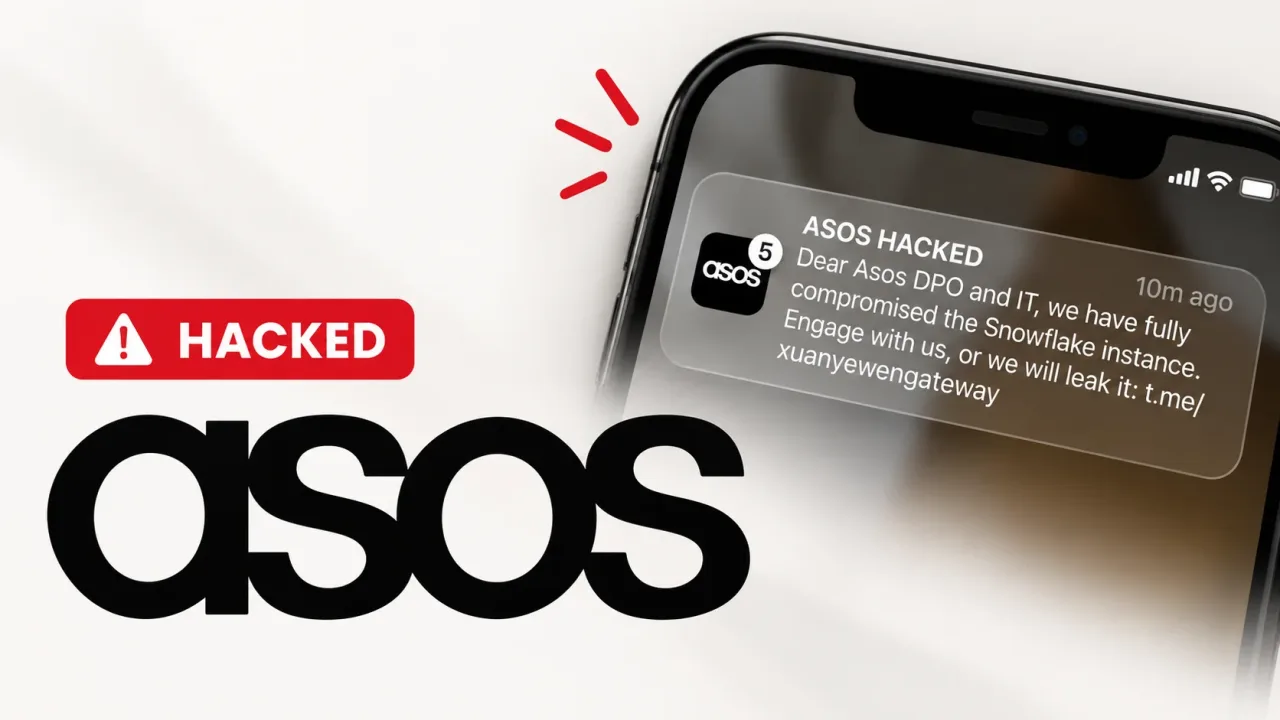
Asos, the UK-based online fashion retailer, is investigating an unauthorized notification sent to customers via its mobile app, which claimed hackers had “fully compromised” its Snowflake data environment. The message, received at around 10 am on October 6, 2026, directed recipients to a Telegram link and warned of potential data leaks unless the company engaged with the attackers. The incident has triggered immediate action from Asos, including restricting access to third-party communication platforms and collaborating with cybersecurity specialists and authorities.
Unauthorized Notification and Initial Response
The notification, titled “ASOS HACKED,” addressed the company’s data protection officer and IT team directly, using a customer communication channel to deliver a public threat. The message stated, “We have fully compromised the Snowflake instance. Engage with us, or we will leak it,” followed by a link to a Telegram account. While the screenshot of the message was shared by multiple outlets, it does not confirm the claimed database compromise. Asos confirmed the presence of “unauthorised activity involving third-party platforms” but emphasized that the Snowflake instance’s status remains unverified.
The company stated that basic personal information, including names and contact details, may have been accessed, though it reiterated that payment-card data and account passwords were not impacted. “We are investigating unauthorised activity involving third-party platforms that we use to communicate with customers,” Asos said in a statement. “We took immediate action to restrict access to the notification platforms and are working with our internal and external specialist advisers, as well as all relevant authorities.”
The National Cyber Security Centre (NCSC), part of GCHQ, has offered assistance, while cybersecurity firms like Check Point and NordVPN have analyzed the threat. Charlotte Wilson of Check Point suggested the attackers might aim to pressure Asos through public exposure, noting that the claimed Snowflake access has not been verified. Marijus Briedis of NordVPN called the message “unusually brazen,” highlighting the risk of phishing attacks following high-profile incidents.
Uncertainty Surrounding Data Breach
The incident has raised questions about the scope of the breach. Snowflake, a cloud data platform used by many businesses, stores information such as transaction records, demographic data, and customer preferences. While the attackers claimed to have accessed its “Snowflake instance,” cybersecurity experts caution that unauthorized access to a notification platform does not necessarily imply access to cloud databases or payment systems.
Rob Demain of e2e assure noted that the compromise could be limited to customer engagement or marketing systems, which are connected to Asos’s data infrastructure. “If the attackers only accessed that layer, it could explain the app notifications, but doesn’t prove any access to the wider retail infrastructure or the claimed data theft,” he said. Laura Tyrylyte of NordVPN emphasized that while the message was alarming, customers should avoid assuming their payment details were stolen, as no evidence has been confirmed.
The incident also coincides with a previous breach in July 2026, when compromised login credentials were used to access customer accounts. That incident, attributed to credential stuffing, exposed names, addresses, phone numbers, and limited payment card details. Asos blocked affected accounts and required password resets, but no direct link has been established between the two events.
| Event | Details |
|---|---|
| Date of Notification | October 6, 2026, at around 10 am |
| Claimed Breach | Compromise of Snowflake instance; unverified |
| Information Potentially Accessed | Basic personal details (names, contact info) |
| Payment Data | Not believed to be impacted |
| Market Reaction | Shares fell over 10%, later recovering slightly |
Market Reaction and Previous Incidents
The incident has already affected Asos’s stock, with shares dropping more than 11% on October 6. The company’s website and app remained operational, but the breach has intensified scrutiny of its cybersecurity measures. Asos, which owns brands like Topshop and Miss Selfridge, is undergoing a major turnaround to reverse declining sales. The incident adds to a series of cyberattacks targeting UK retailers, including Marks & Spencer and Harrods, which faced disruptions and financial losses in recent years.
Cybersecurity experts have also raised concerns about the broader implications of the breach. The Xuanye Group, the alleged attackers, has not been previously documented in hacker forums, though Sophos noted that new groups often emerge to exploit high-profile opportunities. Dray Agha of Huntress warned that sending ransom demands directly to consumer devices is an aggressive tactic designed to force quick negotiations. “I strongly advise shoppers to watch out for targeted phishing attempts while we wait for official confirmation of a data breach,” he said.
Customer Guidance and Ongoing Investigation
Asos has urged customers to avoid clicking on the Telegram link and to follow official updates. It also advised users to monitor their accounts for suspicious activity and to avoid reusing passwords across platforms. Laura Tyrylyte of NordVPN emphasized that while the threat was alarming, customers should not assume their data was compromised. “None of that is information you can easily change once it’s out,” she said, referring to details like order history and addresses.
The investigation is ongoing, with the NCSC assisting in assessing the breach’s scope. Asos has not yet disclosed the full extent of the incident, but its cybersecurity and business continuity insurance may mitigate financial risks. The company has also faced pressure to clarify whether the breach was linked to its previous July 2026 incident, though no evidence has emerged to support such a connection.
Frequently Asked Questions
What information may have been accessed in the breach?
Asos stated that basic personal information, including names and contact details, may have been accessed. Payment-card data and account passwords are not believed to have been impacted.
What should customers do to protect themselves?
Customers are advised to avoid clicking on links in unexpected messages, use unique passwords, and monitor their accounts for suspicious activity. Asos has also urged users to follow official updates through its app or website.
Is there a connection to Asos’s previous cyber incident?
No confirmed link has been established between the current breach and the July 2026 incident, which involved credential stuffing. Asos has not indicated a direct connection between the two events.
The next critical step in the investigation will be determining whether the breach extended beyond third-party communication platforms and into Asos’s broader systems. As the NCSC continues its assessment, customers and investors will be closely watching for further updates. Meanwhile, cybersecurity experts warn that the incident underscores the growing risks of targeting customer communication channels, which can be exploited to amplify the impact of cyberattacks.